Dubai DESC and FAA sign MoU to align cybersecurity and audit oversight
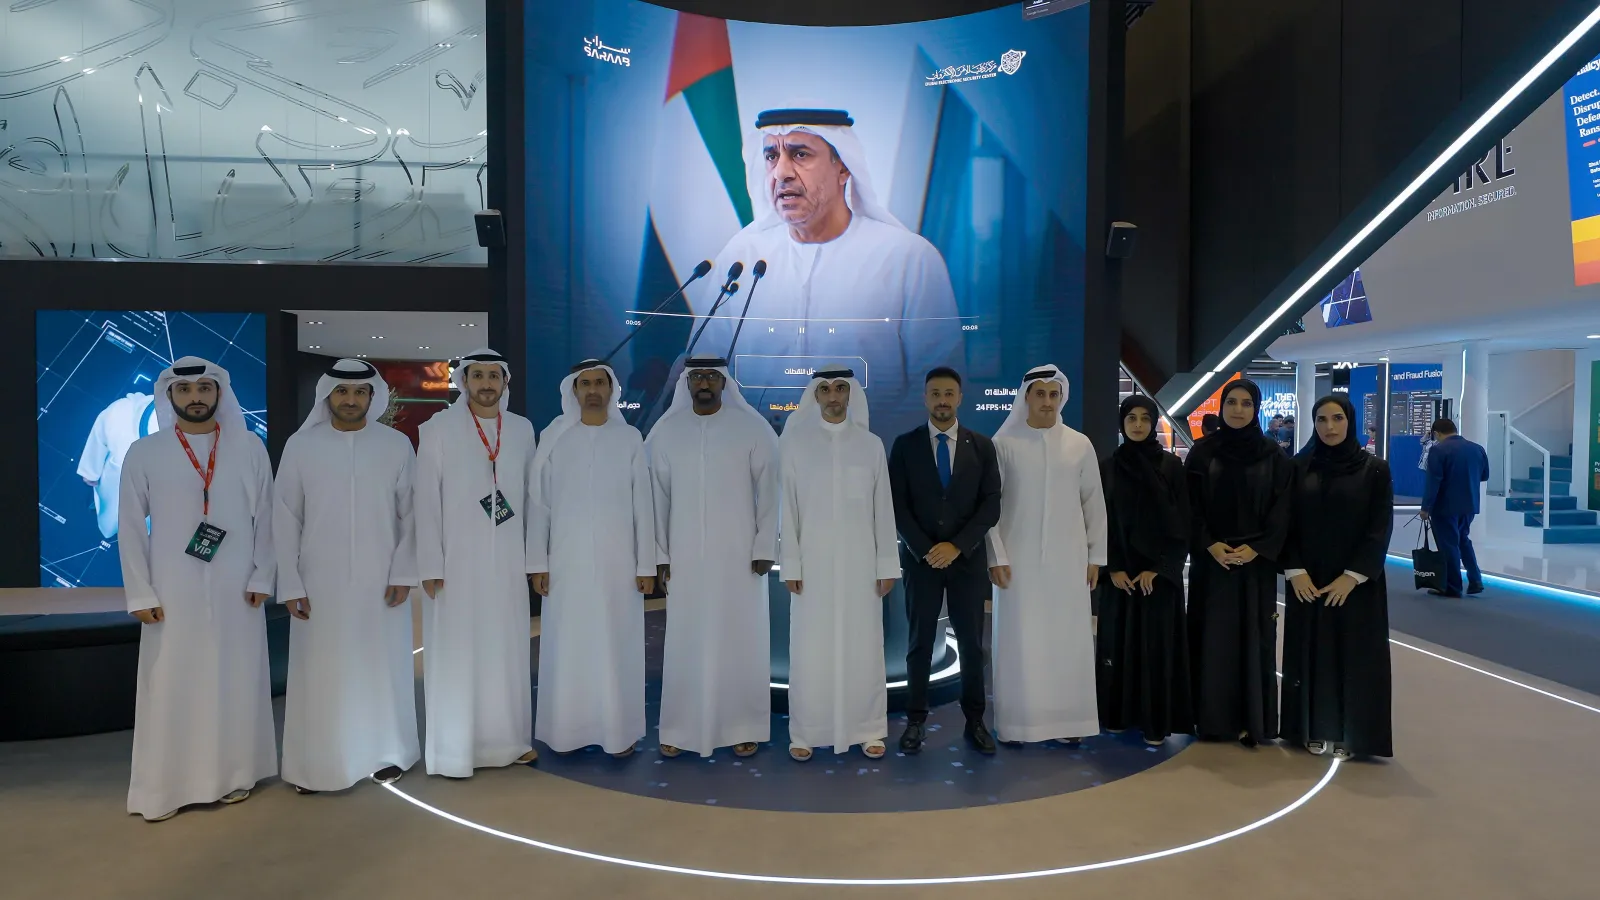
The Dubai Electronic Security Center (DESC) and the Financial Audit Authority (FAA) have signed a Memorandum of Understanding aimed at deepening collaboration across cybersecurity, audit and compliance functions. The agreement was signed by Abdulrahman Al Hareb, Director General of the FAA, and Yousuf Hamad Al Shaibani, Chief Executive Officer of DESC, on 16 September 2026.
Under the MoU, the two entities will exchange technical and professional expertise in audit, oversight and compliance assessment, share planning and reporting methodologies, and co-develop procedural frameworks and guidelines. They will also organise joint training programmes, workshops and joint participation in sector conferences.
The agreement
Al Hareb framed the partnership as part of a broader effort to build an oversight ecosystem capable of keeping pace with rapid digital transformation. "Effective oversight depends not only on the strength of tools and methodologies, but also on the integration of expertise, knowledge exchange and the ability to leverage specialised capabilities across government entities," he said.
Al Shaibani, for his part, described cybersecurity as a shared responsibility requiring unified effort across public institutions, positioning the MoU as a step towards proactive protection of Dubai's digital assets. Neither executive disclosed specific deliverables, timelines, or budget commitments attached to the agreement.
Market and regulatory context
The MoU sits within a wider pattern of Gulf state governments formalising institutional cybersecurity governance. The UAE's national cybersecurity strategy, overseen by the UAE Cybersecurity Council, has pushed individual emirates and federal entities to harmonise controls and audit frameworks since its 2019 update. Dubai specifically has been building out DESC's remit as the emirate's central authority for digital security standards, making inter-agency MoUs a practical mechanism for aligning controls without creating new statutory bodies.
Internationally, the convergence of audit functions and cybersecurity oversight is gaining momentum. Frameworks such as ISO 27001 and ISAE 3402 already embed information-security controls into assurance engagements, and regulators in the EU (under DORA and NIS2) and the UK (via the FCA's operational resilience rules) are requiring audit and compliance teams to engage directly with cybersecurity risk assessment. Gulf jurisdictions are increasingly mirroring these standards as multinational firms demand comparable assurance from regional government counterparties.
For DESC, the partnership with a financial audit body is notable because public-sector financial audit trails increasingly intersect with digital forensics: procurement fraud, data integrity and system access logs are all relevant to modern government audit. Embedding cybersecurity expertise directly into audit workflows, rather than treating them as parallel functions, reflects a maturing approach to government digital risk.
The MoU does not carry legal force beyond the two signatory bodies and sets no binding targets. Whether it produces lasting operational change will depend on the governance structures both entities put in place to track joint workstreams. Observers will look for published joint frameworks or training cohort numbers as early indicators of progress.